Start by installing the SDK and adding the activation example for your language. Run it when your application starts (for example, Form_Load for desktop apps), when the user enters or changes a license key, and periodically if your licensing model requires it. Already have the SDK installed? Jump to the activation example.

Getting started

1

Add client SDK/library

First, we need to install the client SDK / library

Install Nuget package

In Visual Studio package manager
Using dotnet CLI
If you are targeting Mac, Linux or Unity/Mono, we recommend to use the cross platform version of that package.In Visual Studio package manager
Using dotnet CLI
2

Add namespace

3

Add key verification script

Replace ProductId, RSAPubKey, Access Token, and licenseKey with your values, then run the example. This demonstrates activation; additional license checks are explained after the examples.
.NET(C#/VB.NET) only: If your application will run in Unity/Mono, Rhino/Grasshopper or on a platform other than Windows, we recommend to use a different version of Key.Activate.
RSAPubKey is your account’s RSA public key from the dashboard QuickStart Credentials section. Replace the placeholder with your key; see Where do I find my RSA public key?.Your access token needs the Activate permission for these requests. Restrict it to the application’s product. Add the Deactivate permission if the application releases devices, and the GetKey permission if it calls that method. See the application configuration.ProductId is found on the product page and if you add the key verification script to a new product, this value needs to be changed in the code.LicenseKey is found on the product page and contains 20 characters of the following format AAAA-BBBB-CCCC-DDDD. Each end user/customer should normally receive their unique license key. The license key should not be hard coded inside the application. Instead, there should be a way for the user to enter it inside the application or other means.
Using license keys is only one of the ways to authenticate customers. You can also use license files (see the Offline verification tutorial) or a username and password (see the User verification tutorial).

FAQ

Both can return signed information. For direct API requests, request signing with Sign=true; SDK behavior varies, so follow the relevant SDK’s signing flow. GetKey can successfully return a blocked license. Check its Block field instead of treating retrieval success as authorization. An access token can have both permissions; see Access tokens and RSA public key.
No. Your SDK already performs some checks, but your application needs to check the other license properties it relies on. The checks below apply whether the response comes from the API, a saved response, or a manually delivered file:Your application should specify its expected product ID and which checks to apply. It should not take these settings from the file it is checking. Make sure the response includes all fields needed for those checks. Expiry and other time limits also need to be checked while the application stays open, including when it resumes after sleep.
If you want to check once per day, your application can request fresh license information daily and use the saved response between requests. That response must still pass the license checks, including expiry and its age, while the application runs.How often you check, and how long you allow offline use, depends on your product. The offline verification example shows how to save responses and handle connection failures. An older response must not be used to bypass an API rejection, a failed license check, or an SDK error whose cause is unknown.For floating licenses, renew with Activate before the seat expires and stop licensed work at the last confirmed deadline. A daily GetKey call or a cached file does not renew that seat.

Troubleshooting

General

In most cases, this is because some of the required parameters are missing. These are:
  • RSAPubKey
  • auth
  • ProductId
It can also be that the licenseKey is missing. Check the credential guide and the SDK’s error details. A null result alone does not identify the cause and must not automatically enable offline fallback.
Activate rejects a blocked license; depending on the SDK, this may be exposed as a null result or an error. GetKey can return its information successfully, so check Block yourself.

.NET specific (C#/VB.NET)

In some Windows environments (e.g. when developing Excel addins), it might not be feasible to call Helpers.GetMachineCode on .NET Framework 4.6. The reason for this is the call we make to System.Runtime.InteropServices.RuntimeInformation.IsOSPlatform. To fix this, we have added a boolean flag in Helpers class. Before calling Helpers.GetMachineCode or Helpers.IsOnRightMachine, please set Helpers.WindowsOnly=True.
If the approach above does not work, please try the following call instead:
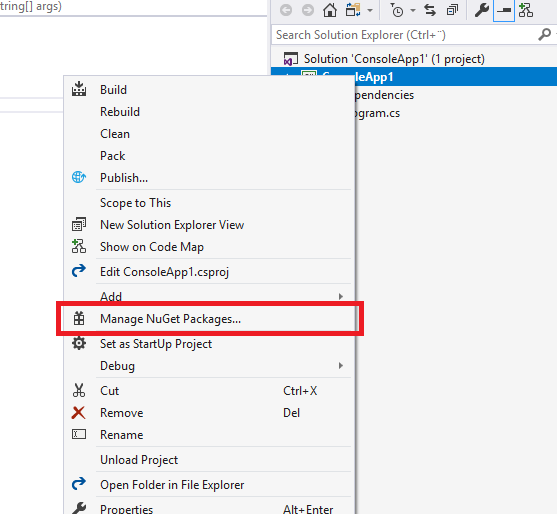
This means that Cryptolens.Licensing library was not included into the project. It can be easily added using NuGet packager manager, which you can find by right clicking on the project:Nuget Vs2017 Example Pn
If you are
If your clients are able to visit app.cryptolens.io and api.cryptolens.io in Microsoft Edge but unable to activate the application, the issue could be both that they are using a proxy, connect to Active directory or that their IT department has blocked TLS of certain versions.To fix these issues, we recommend to:
  1. Update to the latest version of the SDK.
  2. If you run a version of .NET Framework prior to .NET Framework 4.7, we recommend to manually specify which TLS should be used. Before any call to the API (for instance, Key.Activate performs an API call), we recommend to add the following line:
Ideally, you should try to pick the highest available TLS version, but it is important to also test that such TLS version is supported in the .NET Framework vesion that you use.If possible, the best approach is to run the latest version of .NET Framework. If that is not possible, please use at least .NET Framework 4.7. In other cases, the workaround above can be used (i.e. manually specifying the TLS version).
Some customers have reported an error with the right version of Newtonsoft.Json not being found. It seems to be localized to those that target .NET Framework 4.8, and the following error is shown:
The error is thrown when a wrong version of Newtonsoft.Json is installed in the same project as Cryptolens.Licensing library. To fix this, you need to make sure that Newtonsoft.Json is uninstalled completely and then re-install Cryptolens.Licensing.

Python

This error occurs when the timestamp for the expiration date received from the server exceeds the limit in Python. This typically occurs when the Period is set to a excessively large value, often to prevent the license from expiring.While Cryptolens requires a period (defaulted to 30) during the creation of a new license, this does not mark the license as time-limited. You can learn more about it here. In essence, a license is treated as time-limited by either enforcing this in the Python code (e.g. if F1=true, the license is time-limited and so we check the expiration date against the current date, to see that it is still valid) or on the server side. On the server side, you can, for example, set up a feature that will automatically block expired licenses. You can read more about it here.In sum, to solve this issue, you can either follow one of the methods described above or set the period to a smaller value.
This error is thrown when the urllib library (a built in library in Python that we use to send HTTP requests) is unable to locate the CA files on the client machine. From our experience, this error occurs exclusively on Macs where the Python environment is incorrectly installed.To solve this temporarily for testing purposes, you could temporary disable SSL verifications as described in here, however, we do not recommend this in a production scenario. Instead, a better solution is to fix the underlying issue preventing the Python environment from finding the CA files.This can be accomplished in at least two ways:Using certifiBefore calling any of the API methods (e.g. Key.activate), you can add the following code:
Please note that this requires certifi package to be installed.Running a script in the Python environmentAn alternative is to run script in their environment that should fix the issue. You can read more about it in this thread: #65SummaryThe key takeaway is that it is better to address the issue with missing CA on the user side, since this issue will typically be user-specific. If that is not possible, you can use the code above to manually set the path to CA files. Although we have mentioned turning off SSL verification temporarily, it should not be used in production. Key.activate takes care of signature verification internally, but some other methods do not.
If you have customers who want to use a proxy server, we recommend enabling the following setting before calling any other API method, such as Key.Activate.
This will ensure that the underlying HTTP library (urllib) used by Cryptolens Python SDK will use the proxy configured on the OS level. The goal is to make this default behaviour in future versions of the library, once enough feedback is collected.
SSL verification can temporarily be disabled by adding the line below before any call to Key.Activate.
The Cryptolens Python SDK will verify that the license information has not changed since it left the server using your RSA Public Key. However, we recommend to keep this value unchanged.

C++

How errors are reported in the C++ library is described in the README.md file, which is also available here. If you are on a Unix based system, you can find a summary of all curl errors here.